HTTPS is the protocol that protects data exchanged between a browser and a server using TLS, reducing the risk of eavesdropping, tampering, or interference with data as it travels across the network. Understanding what HTTPS is helps businesses choose the right security approach and build more trustworthy websites. In this article, TOT explains how HTTPS works, distinguishes HTTP from HTTPS, clarifies the role of SSL/TLS and security certificates, and shows you how to migrate a website from HTTP to HTTPS.
>>> Read more:
- Security errors when accessing a website: Causes and how to fix them
- What is DNS over HTTPS? Understanding how DoH works
- What is RFI? The role of a request for information in business
- 25 effective ways to fix website errors that prevent access
What is HTTPS?
HTTPS (HyperText Transfer Protocol Secure) is the version of HTTP transmitted over a connection protected by TLS (Transport Layer Security), which secures the data exchanged between a client and a server. According to the IETF, HTTPS is essentially HTTP running on top of a TLS layer, meaning HTTPS is not a completely different protocol from HTTP but rather HTTP with an added security mechanism. The “S” in HTTPS stands for “Secure”, reflecting a connection protected against risks on untrusted networks. Modern TLS provides three important properties for a connection: encryption (encryption), integrity, and authentication
HTTPS is used to encrypt data transmitted between the browser and the server, authenticate the server’s identity, and detect any data that is altered during transmission. As a result, HTTPS reduces the risk of an attacker eavesdropping on information or interfering with the connection in a Man-in-the-Middle (MITM) attack. The Mozilla Developer Network (MDN) likewise defines TLS as protecting a connection through three core mechanisms: encryption, authentication, and data integrity. This is why HTTPS is especially important for websites with logins, forms, transactions, or that handle user data.
On a website, HTTPS is usually recognized directly by the “https://” at the start of the URL, for example “https://example.com”. The https portion of the URL tells the browser that the resource is transmitted using HTTP but through a secure TLS channel. When visiting an HTTPS website, the browser can also display a security icon and let users inspect the website’s certificate information.
HTTPS applies not only to HTML pages but should also be used for resources such as images, JavaScript, and CSS to avoid Mixed Content. For a modern website, therefore, HTTPS should be implemented throughout the entire process of loading and exchanging data.
>>> Learn more:
- What is website security? Its importance and how to keep a website safe
- What is CSRF? Attack techniques and how to effectively prevent CSRF
- A detailed guide to the best way to secure a WordPress website
How does HTTPS work?
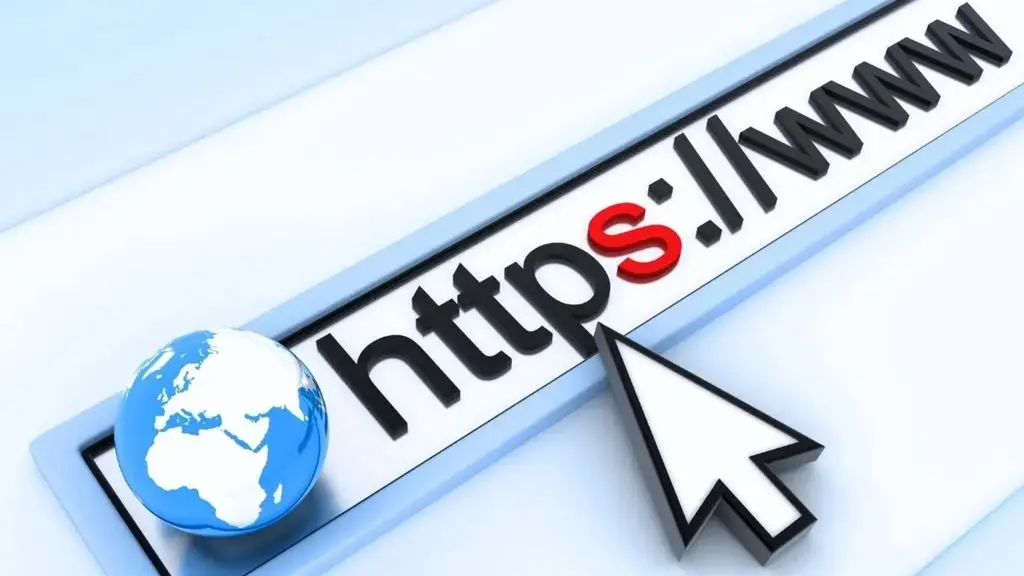
HTTPS works by combining HTTP with TLS (Transport Layer Security) to create a protected data channel between the browser and the server. When a user visits an address beginning with “https://”, the browser does not immediately send HTTP data the usual way; it first establishes a TLS connection with the server.
During this process, the two sides perform a TLS handshake to exchange security information, verify the server’s identity, and agree on the parameters needed for the session. Once setup is complete, HTTP data such as requests, responses, cookies, or form information is transmitted over the TLS connection and encrypted.
Step 1 – The browser requests an HTTPS connection
When a user types “https://example.com” into the browser, the browser recognizes this as an HTTPS address and begins establishing a secure connection with the corresponding server. Before any website data is exchanged, the browser and server need to agree on how to protect the connection using TLS.
In the initial stage, the client sends the information needed to start the TLS handshake, such as the supported TLS versions and suitable cipher options. The server responds with the information needed to continue the setup process. The key point is that the actual HTTP request is only transmitted after the TLS channel has been established, rather than sending application data over an unprotected connection.
Step 2 – The TLS handshake takes place
The TLS handshake is the process that lets the client and server establish security conditions before exchanging data. You can think of it as a “security agreement” step between the browser and the server.
During this process, the client and server exchange the necessary information, including their TLS support and cryptographic parameters. The server sends a digital certificate to the browser. The certificate contains the server’s identifying information and public key, and is signed by a trusted Certificate Authority (CA).
The browser then checks the certificate against several factors such as the domain name, validity period, and certificate chain. If the certificate is valid and matches the website being accessed, the handshake can continue. After that, the client and server agree on the security parameters to use for the session.
The TLS handshake is not meant to transmit website content but mainly to establish the conditions needed to create a secure connection. Once the handshake is complete, both sides have the basis to exchange data while limiting the risk of a third party reading or altering it in transit.
Step 3 – Establishing the session key
After authenticating and agreeing on the security parameters, the client and server use TLS’s cryptographic mechanisms to establish a shared secret, from which they derive the keys used for the session. Users don’t need to understand the underlying algorithms in detail; what matters is that this key is used to protect data during transmission.
Once the session key is established, application data can be encrypted before being sent over the network. Session encryption makes data processing more efficient than using asymmetric cryptography for the entire volume of exchanged data.
Put simply, this process is like the browser and server agreeing on a “session key” that only the two connected parties can use. After that, the HTTP data is protected using the keys and algorithms agreed upon during the TLS session.
Step 4 – Data is transmitted over the TLS connection
Once the TLS handshake is complete and the session key has been established, the browser can send the HTTP request over the secure connection. The server processes the request and returns the HTTP response to the browser, also through the TLS connection.
The transmitted data is protected against unauthorized reading or modification during transit. As a result, information such as login credentials, form contents, cookies, or other application data is not transmitted as plain HTTP over the wire.
The entire HTTPS process can be visualized as follows:
Browser → HTTPS Request → TLS Handshake → Certificate verification → Session key establishment → Encrypted HTTP Data → Web Server → Encrypted HTTP Response → Browser
The key thing to remember is that HTTPS does not replace HTTP. HTTP is still responsible for defining how the browser and server exchange requests, responses, and application data. TLS adds a layer of security to that transmission. So, in short: HTTPS = HTTP running over a connection protected by TLS.
Thanks to this mechanism, HTTPS provides three important security properties: data encryption, server authentication, and data integrity. This is also why HTTPS has become the common standard for modern websites, especially for pages with logins, forms, user accounts, or online transactions.
>>> Read more:
- What is Vulnerability Assessment? A solution for evaluating security vulnerabilities
- What is WCAG? Principles for website content accessibility
- How much does the latest mobile app design and maintenance cost?
What is HTTP?
HTTP (HyperText Transfer Protocol) is the hypertext transfer protocol used to exchange resources and data between a browser or client application and a web server. HTTP operates on a client-server model and is based on a request-response mechanism.
When a user visits a URL, the browser first determines the server address, establishes a suitable network connection, and then sends an HTTP Request to request the resource. The server receives and processes the request, then returns an HTTP Response containing the content or status information. The browser continues to parse the response and may send additional requests to load CSS, JavaScript, images, or other resources.
How does HTTP work?
The HTTP process can be understood simply through the following steps:
Step 1 – The browser sends a request: When a user visits an address such as “http://example.com”, the browser determines the resource it needs to retrieve and sends an HTTP Request to the server. The request may include a method such as GET to retrieve data or POST to send data, along with information such as the URL, HTTP headers, and any accompanying data if needed.
Step 2 – The web server processes the request: The server receives the request, identifies the resource, or performs the corresponding task. For example, for a GET request to the homepage, the server might locate an HTML file or run application logic to generate the content to return.
Step 3 – The server sends an HTTP Response: After processing, the server sends a response back to the browser. The response usually includes a status code such as 200 when the request succeeds, 404 when the resource is not found, or 500 when the server encounters an error. The response may also contain HTML, JSON, images, or other data.
Step 4 – The browser processes the response: The browser reads the response and displays the content to the user. If the HTML references CSS, JavaScript, images, or other resources, the browser continues to send the corresponding HTTP Requests to load them.
Is HTTP secure?
HTTP itself does not provide a TLS encryption layer to protect data during transmission. As a result, HTTP content can be observed or interfered with by a third party if the connection is intercepted on an untrusted network. For instance, if a user submits information through a website that uses only HTTP, the data transmitted between the browser and server is not protected by TLS encryption.
HTTP is therefore not suitable for protecting sensitive information such as passwords, account details, or personal data when transmitted over the Internet. This is the key difference when learning what HTTP and HTTPS are: HTTPS still uses HTTP to exchange data but adds TLS to encrypt the connection, authenticate the server, and ensure data integrity. For modern websites, HTTPS is therefore preferred over plain HTTP.
>>> Learn more:
- What is PCI DSS? The 12 security standards of the payment card industry
- What is DNS over HTTPS? Understanding how DoH works
How do HTTP and HTTPS differ?
HTTP and HTTPS are both used to exchange data between a browser and a web server, but they differ mainly in the security layer of the connection. HTTP transmits data without TLS protection, while HTTPS uses TLS to encrypt data, authenticate the server, and ensure integrity during transmission.
So, when learning about HTTP and HTTPS, you can understand it briefly this way: HTTPS still uses HTTP to handle requests and responses, but it runs over a more secure TLS connection. In other words, HTTPS and HTTP are not two entirely independent protocols; HTTPS is HTTP protected by TLS.
HTTP vs. HTTPS comparison table
| Criteria | HTTP | HTTPS |
| Security | No TLS security layer | TLS protects the connection |
| Data encryption | Not encrypted at the HTTP layer | Data is encrypted when transmitted over TLS |
| Server authentication | Does not use a TLS certificate for authentication | Uses a TLS certificate to support server authentication |
| Data integrity | No TLS mechanism to protect integrity | TLS helps detect data altered during transmission |
| Default port | Port 80 | Port 443 |
| URL | http://example.com | https://example.com |
The table above shows that the difference between HTTPS and HTTP lies not in how HTTP handles web content but mainly in how the connection is protected. HTTP can still be used to load pages and exchange data, but that data is not protected by TLS in transit. HTTPS adds this security layer to reduce the common risks of data traveling over the Internet.
Where do HTTP and HTTPS differ most importantly?
Rather than simply concluding that “HTTPS is safer than HTTP”, you can understand the difference between https and http through three core factors:
1. Data encryption
With HTTP, data is transmitted without TLS encryption. If a third party is able to observe the traffic in transit, the exchanged content can be read or analyzed.
HTTPS uses TLS to encrypt data after the secure connection is established. As a result, content such as login credentials, form data, or cookies is better protected when transmitted between the browser and the server. This is one of the key reasons HTTPS has become the standard for modern websites.
2. Server authentication
HTTP does not provide a mechanism to authenticate the server through a TLS certificate. HTTPS uses a digital certificate to help the browser verify that the connection is heading to the correct server or the domain confirmed by the certificate.
This mechanism is especially important against the risk of a Man-in-the-Middle (MITM) attack, in which an attacker tries to sit between the client and server to interfere with the exchange. TLS does not eliminate every form of cyberattack, but server authentication significantly reduces the risk of a user establishing a connection with a fake server.
3. Data integrity
A secure connection must not only keep data confidential but also ensure that data is not modified in transit. HTTPS uses TLS mechanisms to detect data that has been altered or forged during transmission.
For example, when the server sends a resource to the browser, TLS helps ensure that the received data matches the data that was sent. This is the point that explanations of what the HTTP and HTTPS protocols are often overlook when they focus only on “encryption”.
Does HTTPS make a website slower than HTTP?
HTTPS does add processing overhead compared to HTTP, because the connection needs to perform a TLS handshake before application data is transmitted. However, this does not mean an HTTPS website will be noticeably slower in every case.
Modern web technologies have significantly reduced the cost of establishing and maintaining a secure connection. TLS supports session and connection reuse mechanisms, while modern browsers and servers are optimized to handle encryption efficiently. In particular, HTTP/2 and HTTP/3 in practice are usually deployed alongside HTTPS, delivering performance improvements in addition to security.
Therefore, when weighing HTTP and HTTPS, you should not trade away HTTPS just to expect a small gain in speed. For modern websites, data security, server authentication, and connection integrity matter more than the added overhead of TLS. HTTPS should now be seen as the default foundation for a website rather than an option reserved only for payment pages.
>>> Learn more:
- What is Threat Intelligence? A new direction in cybersecurity
- What is XSS? How to test for and effectively prevent XSS attacks
- What is an offshore development center? An optimal solution for businesses
Are SSL, TLS, and HTTPS the same?
SSL, TLS, and HTTPS are closely related but are not three identical concepts. SSL (Secure Sockets Layer) is the security technology that preceded TLS (Transport Layer Security), while HTTPS (HyperText Transfer Protocol Secure) is HTTP transmitted over a connection protected by TLS.
Put simply, TLS is the security protocol, while HTTPS is the way HTTP uses TLS to protect data as it travels between the client and the server.
| Criteria | SSL | TLS | HTTPS |
| Full name | Secure Sockets Layer | Transport Layer Security | HyperText Transfer Protocol Secure |
| Nature | Older security technology/protocol | Security protocol succeeding SSL | HTTP running over a TLS connection |
| Role | Predecessor of TLS | Encryption, authentication, and data integrity protection | Protects HTTP traffic as it travels across the network |
| Current status | Obsolete, no longer recommended | In use | Widely used for modern websites |
| Relationship | Predecessor of TLS | Security layer for HTTPS | HTTP applied over TLS |
What is SSL?
SSL stands for Secure Sockets Layer, a technology developed to protect data transmitted between two parties over a network. SSL creates an encrypted connection, helping to limit the risk of a third party reading or interfering with data during transmission.
However, older SSL versions revealed many security issues and were replaced by TLS. So when people say “SSL certificate” in practice, many are using a familiar term to refer to the TLS certificate that websites use today. Modern websites should not use outdated SSL versions.
What is TLS?
TLS stands for Transport Layer Security, the security protocol that succeeded SSL. TLS protects the connection between a client and a server by providing mechanisms for data encryption, server authentication, and information integrity.
During the process of establishing an HTTPS connection, the browser and server perform a TLS handshake to determine the security parameters and establish the session key. HTTP data is then transmitted over the protected TLS connection.
How is HTTPS related to SSL/TLS?
HTTPS can be understood simply as HTTP + TLS. HTTPS is not a separate encryption protocol that replaces HTTP. Instead, HTTP still handles the exchange of requests and responses, while TLS creates a security layer for that data transmission.
So when you visit “https://example.com”, the browser first establishes a TLS connection with the server, verifies the certificate, and sets up the security mechanism. HTTP requests and responses are then transmitted over the encrypted connection.
You can remember the relationship this way:
SSL → predecessor of TLS → TLS protects the connection → HTTPS uses TLS to protect HTTP.
Therefore, terms like “SSL/HTTPS” or “SSL certificate” remain common, but technically, modern HTTPS mainly uses TLS rather than SSL.
>>> Read more:
- What is SOC? Understanding the Security Operations Center (SOC)
- What is RSA? How RSA encryption works and its use in digital signatures
- What is Brute Force? Causes and how to prevent it effectively
What is an HTTPS certificate?
An HTTPS certificate, commonly called an SSL/TLS certificate, is a digital certificate used to support website authentication and establish a secure HTTPS connection between the browser and the server. When a user visits a website via “https://”, the browser can check the certificate to determine which server the website is connecting to and use the information in the certificate to establish the TLS connection.
The certificate is issued by a Certificate Authority – the organization responsible for verifying information according to the certificate type and signing the digital certificate. When a certificate is valid, unexpired, and matches the domain, the browser can use that information during server authentication.
What is an SSL/TLS certificate used for?
An SSL/TLS certificate plays several key roles in the process of establishing HTTPS:
- Authenticating the website’s identity: The certificate contains domain information and identifying data that the CA has verified according to the certificate’s level. This helps the browser check whether the server it is connecting to matches the domain being accessed.
- Providing the public key: The certificate contains the server’s public key, which is used in TLS’s cryptographic mechanism.
- Supporting TLS connection setup: During the TLS handshake, the browser and server use the certificate along with the related security mechanisms to authenticate and establish a protected connection.
- Providing the basis for the browser to verify the server: The browser checks the certificate based on the domain, validity period, CA signature, and certificate chain to determine whether the connection meets the security requirements.
Common types of SSL/TLS certificates
Depending on the scope of validation and the number of domains that need to be protected, some common certificate types include:
| Certificate type | Characteristics |
| DV (Domain Validation) | Verifies control of the domain; usually issued quickly and suitable for many general websites. |
| OV (Organization Validation) | Verifies the domain and some information about the organization behind the website. |
| EV (Extended Validation) | An extended organization validation process according to the CA’s requirements and applicable standards. |
| Wildcard | Protects a domain and its matching subdomains, for example: “*.example.com”. |
| Multi-domain | Allows a single certificate to protect multiple domains or hostnames within the issued scope. |
These types can serve different needs. For example, Wildcard is suitable when a business needs to protect many subdomains, while Multi-domain is useful when one system manages multiple domains.
Does an HTTPS website mean it is definitely safe?
No. HTTPS does not mean a website is 100% safe. HTTPS mainly protects the connection between the client and the server, helping to encrypt transmitted data, support server authentication, and ensure data integrity during transmission.
A website can still contain malware, security vulnerabilities, fraudulent content, or dangerous behavior even when it uses HTTPS. Even a fake website can be issued a certificate for a domain that a malicious actor controls.
Therefore, the padlock icon or “https://” should be understood as a signal of a protected connection, not a guarantee that the entire website is trustworthy. Users and businesses still need to combine HTTPS with other measures such as server security, software updates, access control, and website monitoring.
>>> Learn more:
- What is a security vulnerability? Understanding website vulnerabilities and how to prevent them effectively
- What is OWASP? The top 10 security vulnerabilities and risks according to OWASP
- What is Cyber Security? A roundup of the 9 most common types of Cyber Security today
What benefits does HTTPS bring to a website?
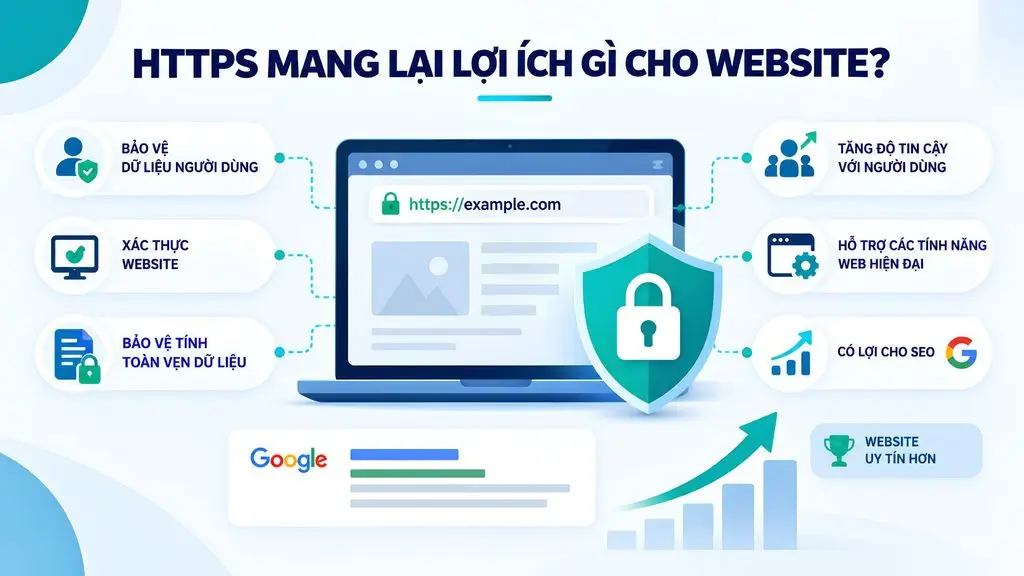
HTTPS not only helps a website display a secure connection icon in the browser but also plays an important role in protecting data, authenticating the server, and maintaining information integrity when transmitted over the Internet.
For business websites, e-commerce sites, login platforms, or any system that handles user data, HTTPS should be considered a basic security standard. In addition, HTTPS supports many modern web features and is one of the signals Google uses in its ranking system.
Protecting user data
One of the most important benefits of HTTPS is encrypting data during transmission. When users log in, fill out forms, submit contact information, or complete transactions, the data is transmitted over a TLS connection instead of plain HTTP.
The encryption mechanism helps reduce the risk of a third party reading information while the data is moving between the browser and the server. This factor is especially important for sensitive data such as account information, personal information, or transaction data.
Authenticating the website
HTTPS uses an SSL/TLS certificate to support server authentication. The browser can check the certificate, domain, validity period, and certificate chain to determine that the connection is being established with the correct server.
This mechanism helps reduce the risk of users being redirected to or connecting with a fake server in Man-in-the-Middle attacks.
Protecting data integrity
HTTPS not only encrypts data but also helps protect data integrity during transmission. If data is altered without authorization in transit, TLS security mechanisms can detect the anomaly rather than letting the information be silently modified.
This protection mechanism helps limit situations where website content, requests, or responses are tampered with while traveling between the client and the server.
Building trust with users
Modern browsers increasingly emphasize the security status of a connection. A website that uses HTTPS helps users recognize that the data they exchange with the website is being transmitted over a protected connection.
For businesses, HTTPS also contributes to a more professional experience, especially for login pages, contact forms, online stores, and platforms that ask users to enter information.
Supporting modern web features
HTTPS is also the foundation for many modern web features that require a secure context. Some APIs and browser capabilities only work fully when the website is served over a secure connection.
Therefore, implementing HTTPS is not only about protecting data but also helps a website better meet the technical requirements of the modern web ecosystem. This is one of the reasons HTTPS is increasingly seen as the default standard rather than an optional add-on.
Does HTTPS affect SEO?
Yes. HTTPS is one of Google’s ranking signals, but its level of impact should not be overstated. A website using HTTPS does not mean it will automatically rank at the top or surpass competitors with better content, authority, and experience.
The SEO value of HTTPS also lies in creating a stable and secure technical foundation for the website. When migrating from HTTP to HTTPS, businesses need to carry out the migration correctly to avoid affecting crawlability and indexing.
Specifically, you need to set up 301 redirects from each HTTP URL to the corresponding HTTPS URL, and update the canonical, XML sitemap, internal links, and related resource URLs. At the same time, you need to check the redirect chain, crawl errors, and mixed content issues after the migration.
Therefore, HTTPS should be seen as a foundational requirement of a modern website rather than an SEO trick that quickly boosts rankings.
>>> Read more:
- What is SQL injection? 4 effective ways to prevent SQL injection
- What is DDoS? Signs, and how to prevent and handle it effectively
- What is Pentest? What you need to know about penetration testing
When does a website need to use HTTPS?
Technically, any website can use HTTPS, not just those that handle payments or sensitive data. HTTPS helps protect the connection between the client and the server and helps the website meet the security requirements of the modern web environment. Therefore, HTTPS should be implemented from the start rather than waiting until the website runs into a security problem.
You should use HTTPS if your website falls into one or more of the following cases:
- Business websites: A website introducing a company, brand, or service should use HTTPS to protect the connection and create a trustworthy experience for visitors.
- Sales websites: Sales pages often have contact forms, customer information, or ordering functions, so HTTPS helps protect data during transmission.
- E-commerce websites: Websites that handle a lot of account information, orders, and transactions should treat HTTPS as a basic security requirement.
- Websites with login forms: Usernames, passwords, and login session data need to be transmitted over a protected connection to reduce the risk of eavesdropping.
- Websites that collect customer information: Registration, consultation, quote, or contact forms may contain names, emails, phone numbers, and other user data.
- Online payment websites: HTTPS is an important component in protecting the connection when users perform payment-related actions. However, HTTPS does not replace the specialized standards and security measures dedicated to payment systems.
- Websites that use user accounts: Platforms with personal profiles, activity history, private content, or functions that require login should use HTTPS to protect the session.
- Websites that want to use features requiring a secure context: Some APIs and modern web features require a website to be served in a secure context, for which HTTPS is an essential condition.
>>> Learn more:
- 40 effective website security and malware scanning tools
- What is End-to-end encryption (E2EE)? How does it work?
How to migrate a website from HTTP to HTTPS
Migrating a website from HTTP to HTTPS is not simply about installing an SSL/TLS certificate. It is a website migration process that can affect security, accessibility, and SEO if configured incorrectly. Businesses need to ensure HTTPS works on the server, redirect old URLs using 301 redirects, update all internal URLs, and check resources to avoid mixed content.
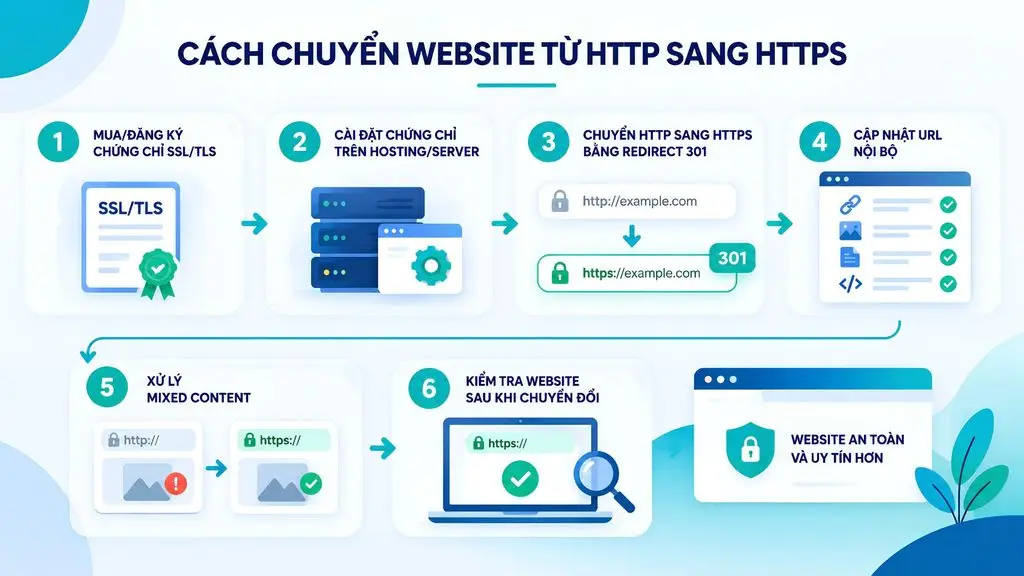
The basic process can be carried out in the following 6 steps:
Step 1 – Buy or register an SSL/TLS certificate
First, the website needs an SSL/TLS certificate that matches the domain. The certificate can be provided by a Certificate Authority (CA), a hosting provider, or deployed through free certificate services.
When choosing a certificate, you need to determine the scope of domains that need protection. A website with a single domain can use a certificate matching that domain, while a system with multiple subdomains or multiple domains may consider Wildcard or Multi-domain.
Before installing, check that the domains in the certificate correctly cover the hostnames the website is using, such as example.com and www.example.com.
Step 2 – Install the certificate on the hosting/server
Once you have the certificate, you need to install the SSL/TLS certificate on the hosting or server where the website runs. Depending on the environment, such as Apache, Nginx, IIS, or a hosting platform, the configuration can differ.
After installation, test the website using the HTTPS URL and confirm that the certificate is valid, unexpired, matches the domain, and has a complete certificate chain. If the website uses a CDN or reverse proxy, you also need to check the TLS configuration at this intermediate layer.
Step 3 – Redirect HTTP to HTTPS using 301 redirects
Once HTTPS is working reliably, set up 301 redirects from each HTTP URL to the corresponding HTTPS URL.
For example:
http://example.com/page → https://example.com/page
Redirects should take users and search engines directly to the corresponding HTTPS version rather than creating multiple redirect steps. At the same time, avoid redirecting all URLs to the homepage if the corresponding HTTPS URL still exists.
Step 4 – Update internal URLs
After the migration, you need to review the entire website to replace HTTP URLs with HTTPS. The important components to check include:
- Internal links: Switch internal links to HTTPS URLs to reduce unnecessary redirects.
- Canonical: Ensure the canonical tag points to the official HTTPS version.
- XML Sitemap: Update the sitemap to use only the HTTPS URLs that need to be indexed.
- Images: Check whether the src, srcset, and image URLs still use HTTP.
- CSS/JS: Switch CSS, JavaScript, and frontend resource files to HTTPS.
- Structured data: Review the URLs in structured data and update them to HTTPS when needed.
In addition, check the URLs in menus, breadcrumbs, hreflang, Open Graph, schema, and any configurations that generate URLs automatically.
Step 5 – Handle Mixed Content
Mixed Content occurs when the main page is loaded over HTTPS but one or more resources inside it are still called over HTTP.
For example: https://example.com
But the image is loaded from:
http://example.com/image.jpg
In this case, the browser may warn about or block some insecure resources. The fix is to switch the resource URL to HTTPS:
https://example.com/image.jpg
You need to review not only images but also CSS, JavaScript, fonts, videos, iframes, and third-party resources. For large websites, you can use a crawling tool to detect any remaining HTTP URLs.
Step 6 – Test the website after the migration
After completing the migration to HTTPS, you need to check the entire website before and after Google re-crawls the URLs. The items to review include:
- HTTPS is working and the certificate is valid.
- HTTP redirects correctly to HTTPS.
- No significant mixed content remains.
- Canonical uses the correct HTTPS version.
- The XML Sitemap contains HTTPS URLs.
- Internal links prioritize HTTPS.
- Search Console is updated and tracking data for the HTTPS version.
- Check for crawl, index, and redirect errors after the migration.
Businesses can also deploy HSTS (HTTP Strict Transport Security) after making sure HTTPS is running reliably. HSTS requires the browser to prioritize HTTPS for subsequent visits, thereby helping reduce the risk of downgrade attacks or SSL stripping. However, HSTS needs to be configured carefully because this policy can make reverting to HTTP difficult when the HTTPS configuration is not yet complete.
>>> Learn more:
- The 10 best AI website design tools with a detailed comparison
- A guide to designing websites with AI – free, paid, and effective
How to check whether a website already uses HTTPS
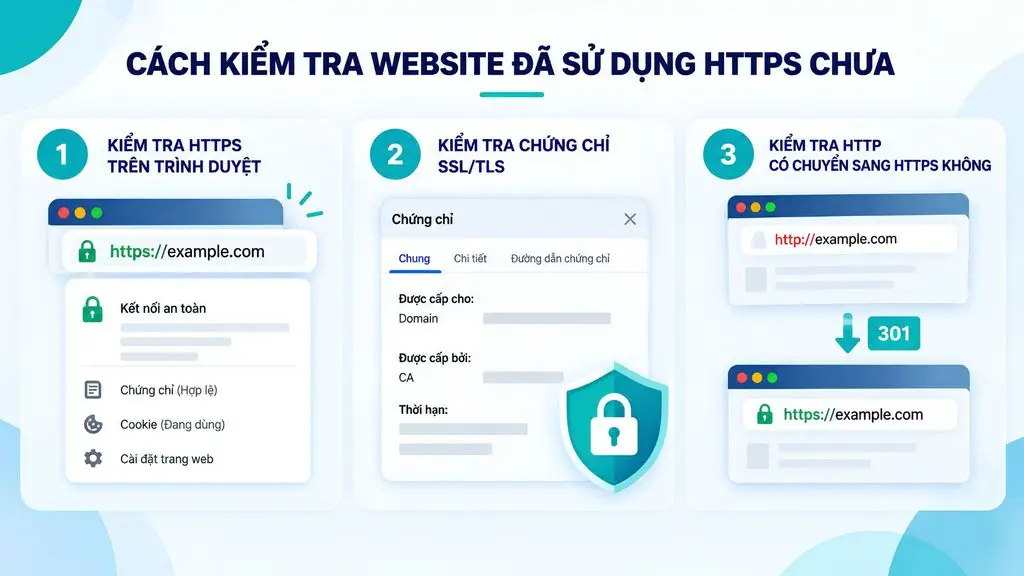
You can check whether a website already uses HTTPS with a few simple actions in the browser and by inspecting the certificate information directly. However, simply seeing “https://” is not enough; you need to confirm that the certificate is valid and check whether the HTTP version is correctly redirected to HTTPS.
Checking HTTPS in the browser
The fastest way is to open the website and look at the URL in the address bar. If the address begins with “https://”, the website is using an HTTPS connection for that URL.
You can also check the security icon next to the URL. When you click this icon, the browser usually provides information about the connection status and the website’s security certificate.
Note that the icon’s appearance can vary by browser. Therefore, you should review the detailed certificate information rather than relying on the icon alone.
Checking the SSL/TLS certificate
In the browser’s security information section, check the key elements of the SSL/TLS certificate:
- Domain: The domain on the certificate must match the website being accessed.
- Validity period: The certificate must be valid and unexpired.
- CA (Certificate Authority): Check the organization that issued and signed the certificate.
- Certificate chain: Ensure the certificate chain is valid and trusted by the browser.
If the certificate is expired, has the wrong domain, or the certificate chain has an error, the browser may display a security warning to the user.
Checking whether HTTP redirects to HTTPS
Besides checking the HTTPS version, you need to confirm that the old HTTP URL is redirected to the corresponding HTTPS URL.
For example: http://example.com → https://example.com
Ideally, the redirect from HTTP to HTTPS uses a 301 and takes the user directly to the corresponding HTTPS URL. For SEO-optimized websites, you should also check important URLs using a crawling tool or by inspecting the HTTP response to detect redirect chains, redirect loops, and URLs that still return HTTP.
>>> Learn more:
- The web content accessibility guidelines WCAG 2.2
- What are the W3C standards? Why should you design a website to W3C standards?
Common HTTPS errors
During the deployment or migration of a website from HTTP to HTTPS, certain errors can cause the browser to display warnings, resources to fail to load, or users to be redirected incorrectly. For business websites, these errors not only affect the experience but can also cause security and Technical SEO problems. Below are the common HTTPS errors to check for.
SSL certificate expired
SSL certificate expired occurs when the website’s SSL/TLS certificate has expired but has not been renewed. In that case, the browser may display a security warning and prevent the user from continuing to access the site.
To handle this, check the certificate’s validity period and renew it before it expires. For important websites, you should set up an auto-renewal mechanism or monitor the validity period to reduce the risk of a certificate expiring unexpectedly.
SSL certificate mismatch
SSL certificate mismatch occurs when the domain a user accesses does not match the domain or hostname protected by the certificate. For example, the certificate is issued only for example.com but the user accesses www.example.com, and that hostname is not within the certificate’s scope.
You need to review the domain/SAN (Subject Alternative Name) list in the certificate and configure a certificate that matches all the hostnames the website actually uses.
Mixed Content
Mixed Content appears when the main page is loaded over HTTPS but some resources are still called over HTTP. For example, the HTML uses https://example.com but images, CSS, or JavaScript are loaded from http://example.com/….
This error can cause the browser to warn about or block insecure resources. The fix is to update all resource URLs to HTTPS and recheck using developer tools or a crawler.
Too many redirects
The Too many redirects error occurs when a website creates too many redirect steps or forms a redirect loop. A common case is HTTP redirecting to HTTPS, but the server or proxy configuration redirects HTTPS back to HTTP.
You need to check the entire redirect chain, especially when the website uses a CDN, reverse proxy, or multiple server layers. The goal is to ensure HTTP is redirected directly to the corresponding HTTPS URL without creating a loop.
The website is HTTPS but some resources still use HTTP
This is a common case after migration. The main website already uses HTTPS but the URLs in images, CSS, JavaScript, fonts, videos, or iframes still use HTTP.
Besides causing Mixed Content, these URLs also mean the website has not fully migrated to HTTPS. You need to crawl the website and find URLs beginning with http://, then update them to the HTTPS version if the resource supports HTTPS.
The HTTP → HTTPS redirect is incorrect
The HTTP → HTTPS redirect can be wrong if the old URL does not go to the correct corresponding HTTPS URL, redirects through too many steps, or all URLs are sent to the homepage.
For example, the appropriate implementation is:
http://example.com/page → https://example.com/page
Instead of:
http://example.com/page
→ https://example.com
→ https://example.com/page
For SEO, you should check the status code, redirect chain, and destination URL to ensure the migration does not lose the signals from the old URLs. After configuring, check the important URLs as well, not just the homepage.
Conclusion
HTTPS helps encrypt data, authenticate the server, and protect user information during transmission. It is an essential standard not only for e-commerce websites but also for business, login, or data-collection pages. When migrating from HTTP to HTTPS, you need to correctly set up SSL/TLS, 301 redirects, canonical, sitemap, internal links, and handle Mixed Content. As a result, a website both strengthens its security and maintains SEO effectiveness while building trust with visitors.
Frequently asked questions about HTTPS
What is HTTPS? What does HTTPS stand for?
HTTPS (Hypertext Transfer Protocol Secure) is the secure version of the HTTP protocol, used to safely transmit data between a web browser and a server. HTTPS is HTTP transmitted over a TLS security layer, which encrypts data, authenticates the server, and protects information integrity when exchanged between the browser and the server. HTTPS is currently the common standard for modern websites.
Why is HTTPS more secure?
HTTPS is more secure than HTTP because it uses TLS to encrypt and protect data during transmission. TLS helps prevent a third party from easily reading the content exchanged between the client and the server, and it supports server authentication and detects data that has been altered without authorization. As a result, HTTPS reduces the risk of eavesdropping, spoofing, or Man-in-the-Middle attacks. However, HTTPS only protects the connection; it does not guarantee that a website is free of malware, fraud, or dangerous content.
What is the difference between HTTP and HTTPS?
HTTP and HTTPS differ mainly in the security layer. HTTP transmits data without a TLS layer to encrypt and authenticate the connection, while HTTPS uses TLS to protect data as it travels between the browser and the server. HTTP typically uses port 80 and URLs beginning with “http://”; HTTPS typically uses port 443 and URLs beginning with “https://”. So, when learning what http and https are, you can understand it simply: HTTPS = HTTP protected by TLS.
What is a website that does not support HTTPS?
A website that does not support HTTPS is one that uses only HTTP or has not configured a valid HTTPS connection. In that case, the URL usually begins with “http://” instead of “https://”, and the exchanged data is not protected by TLS. If the website asks users to log in, enter personal information, or submit data through a form, the lack of HTTPS increases the risk of data being eavesdropped on or tampered with in transit. Modern browsers may also display a warning for HTTP pages, especially when they ask for input.
Is it a problem if a website does not have HTTPS?
A website without HTTPS can still be accessed, but it should not be considered a suitable choice for a modern website. Data transmitted over HTTP is not protected by TLS, increasing the risk of eavesdropping or alteration during transmission. Beyond security concerns, the browser may warn users that some web features requiring a secure context will not work over HTTP. For business, sales, login, or data-collection websites, HTTPS should be implemented by default to increase safety and trust.
How do you migrate a website from HTTP to HTTPS?
To migrate a website from HTTP to HTTPS, you need to install an SSL/TLS certificate and configure the entire website to use HTTPS. The basic process includes: installing the certificate for the correct domain, setting up 301 redirects from HTTP URLs to the corresponding HTTPS URLs, and updating the canonical, sitemap, internal links, and resources such as images, CSS, and JavaScript. Then, check Mixed Content, the certificate, redirects, and crawlability/indexing. For SEO, you should update the configuration in Google Search Console and monitor for errors after the migration.